TL;DR

Get everyday essentials delivered free with Prime
- Fast, free delivery on millions of items
- Prime Video, Amazon Music and more included
- Member-only deals all year
A Bloomberg investigation, summarized by Meduza, describes Russia-linked hacking groups exploiting poorly secured industrial control systems at facilities in the United States and Europe. Reported disruptions included water outages, spoiled meat and factory problems; several suspects or groups face allegations, while the full scale and effects of the attacks remain unclear.
Russia-linked hacking groups have exploited poorly secured industrial control systems to disrupt water facilities, factories and food production in the United States and Europe, according to a Bloomberg investigation summarized by Meduza on October 28. The reported incidents include a water outage affecting hundreds of Danish homes and operational disruptions at U.S. and Spanish businesses; attribution and responsibility vary by incident.
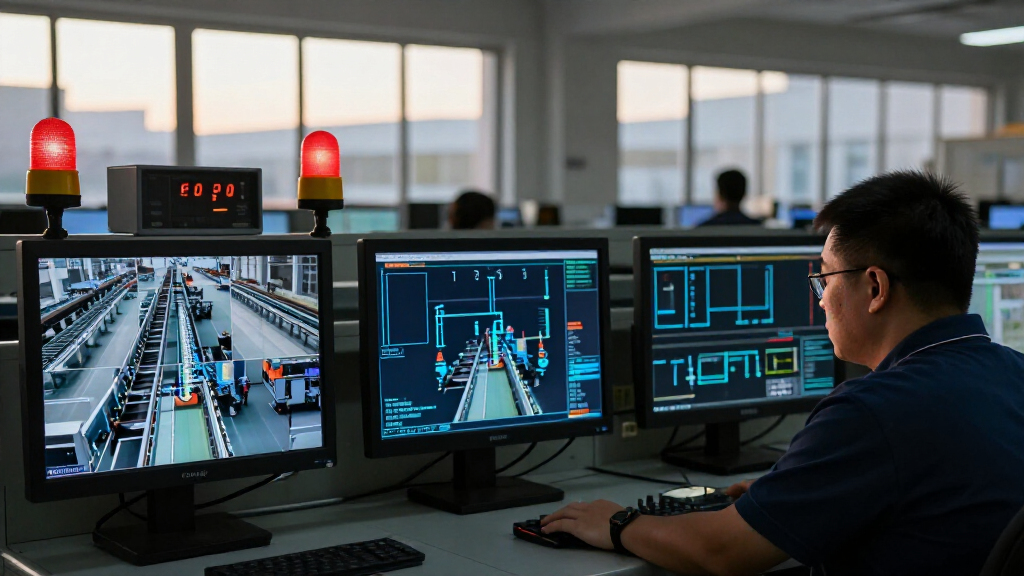
The incidents described in the report show how access to basic control systems can cause physical disruption without highly sophisticated techniques. In December 2024, a water system serving about 450 homes in Tureby, Denmark, lost pressure after its electronic settings were changed. After workers restarted the pumps, pressure surged and underground pipes burst. The pump controller’s manufacturer concluded the system had been hacked. The local water committee chair told Bloomberg the system had been bought cheaply and used the password “1234.”
In the United States, hackers reportedly disabled refrigeration at a meatpacking plant near Los Angeles in 2024, spoiling more than 2,000 pounds of meat. An ammonia leak prompted workers to evacuate. Other reported incidents that year involved altered settings at a Texas public water system, where an unknown volume of water spilled from storage tanks, and tampering with bacteria-killing equipment at a Pennsylvania wastewater facility. Bloomberg also described incidents in Spain between late 2024 and summer 2026, including disrupted crematorium ovens, malfunctioning transformer-manufacturing equipment, and winery heating and ventilation failures.
The report links some attacks to Cyber Army of Russia Reborn (CARR) and Z-Pentest, groups that have publicly claimed involvement in attacks on infrastructure. CISA says Z-Pentest formed in 2024 from members of CARR and another group, and the European Union has sanctioned it over attacks on critical infrastructure. These group-level links do not, on their own, establish who carried out each incident.
Weak Controls Can Disrupt Essential Services
The reported cases show that intrusions into industrial control systems can affect water supply, food safety and factory operations, not just computer networks. A changed pump setting or disabled refrigeration can create physical consequences, including service interruptions, spoiled products, equipment damage and evacuation.
Many of the attacks described appear to have relied on weak security rather than advanced technical methods. That makes the risk relevant to smaller operators as well as major infrastructure companies: systems selected for cost or convenience can become accessible entry points if passwords and remote access are not properly protected. The report does not establish that every incident caused lasting damage, but it documents disruptions with real operational effects.
Popular right now

eufy E25 Robot Vacuum and Mop Combo with HydroJet Roller Mop

Ninja CREAMi 7-in-1 Ice Cream Maker, NC301

Ninja Foodi 10-Quart DualZone 6-in-1 Air Fryer, Black, DZ302
As an affiliate, we earn on qualifying purchases.
From Online Attacks to Industrial Controls
Bloomberg’s report places the incidents within a broader shift following Russia’s full-scale invasion of Ukraine. It says Moscow-linked groups expanded their focus beyond websites and organizations to include critical infrastructure and businesses in Western countries. The examples range from water and wastewater systems to food facilities and manufacturing equipment.
CISA has described CARR as linked to Russia’s military intelligence agency, the Main Directorate of the General Staff, formerly known as the GRU. The agency says some CARR members broke away and formed Z-Pentest, which it characterizes as focused on industrial sabotage. The EU has also sanctioned both groups, according to the source material. Such official assessments and group claims provide context, but they do not confirm responsibility for every specific attack in Bloomberg’s account.
The source also describes a September 2025 test by cybersecurity firm Forescout Technologies. The company said a group called TwoNet broke into a dummy industrial system made to resemble a Dutch water facility and then claimed it had attacked the fictional site. The episode illustrates that attackers may make exaggerated claims; it does not prove an attack on a real water facility.
“I am genuinely surprised that we haven’t yet seen a catastrophe.”
— Cian Heasley, principal consultant at Acumen Cyber
Attribution and Damage Remain Uneven
The source material does not establish who was responsible for every incident, or whether the hackers named in the report directly carried out each intrusion. Some groups have claimed responsibility for attacks, while government agencies have assessed links between groups and Russian entities. Claims by groups and allegations by authorities are not equivalent to independently confirmed attribution.
The full extent of damage is also not specified. For example, the volume of water spilled in Texas is unknown, and the report does not provide a complete accounting of financial losses or lasting service effects across the incidents. Several individuals mentioned face criminal allegations: Ukrainian citizen Victoria Dubranova is in custody and denies the charges, while Italian citizen Chris Barlati has pleaded not guilty and is not currently in police custody. Their cases remain distinct from proof of responsibility for any particular facility attack.
Operators and Investigators Face Follow-Up
The next steps will depend on ongoing investigations and on whether affected operators disclose further technical findings. The source material does not provide a timetable for new charges, court proceedings or official updates on the incidents. Authorities and facility owners may clarify which systems were accessed, how long attackers retained access and what changes were made afterward.
For operators, the reported cases point to practical security measures: replace default or guessable passwords, restrict remote access, monitor control systems for unexpected changes and maintain procedures for restoring safe operation. These steps do not establish that future attacks will be prevented, but they address weaknesses identified in the incidents described.
Key Questions
What did the hackers reportedly target?
The Bloomberg report describes attacks affecting water and wastewater systems, food production, wineries, crematorium equipment and manufacturing in the United States and Europe.
Were all of the attacks attributed to Russia?
No. The report describes groups assessed as Russia-linked and notes public claims of responsibility, but it does not establish attribution for every incident. Some claims and allegations remain unverified or subject to investigation.
What happened to the Danish water system?
In December 2024, about 450 homes in Tureby lost water after a control setting was changed. When workers restarted the pumps, pressure surged and underground pipes burst. The controller’s manufacturer concluded the system had been hacked.
Have the named suspects been convicted?
The source says Victoria Dubranova denies the charges and is in custody. Chris Barlati has pleaded not guilty and is not currently in police custody. The material does not report convictions.
Source: meduza.io